01
WATCH
Continuous visibility across your environment.
NightGrid monitors telemetry across the endpoints, identities, cloud services, networks and infrastructure connected to your security environment.
 Know when something changes.
 Request a security review
Continuous security operations
NightGrid gives organisations continuous visibility across their security environment—backed by analysts who know what deserves action.
WATCH. DETECT. DEFEND.
 24/7 MONITORING
 HUMAN-LED ANALYSIS
 RAPID ESCALATION
 GLOBAL VISIBILITY
THE THREAT LANDSCAPE DOES NOT KEEP OFFICE HOURS
Cyber threats often begin with something almost invisible: an unusual login, an unexpected process or an endpoint behaving differently.
NightGrid provides the continuous oversight needed to find those signals before security events become business incidents.
02 / OPERATING MODEL
Technology gives you signals. NightGrid turns those signals into visibility, judgement and action.
01
Continuous visibility across your environment.
NightGrid monitors telemetry across the endpoints, identities, cloud services, networks and infrastructure connected to your security environment.
Know when something changes.

02
Turn security noise into actionable intelligence.
Events are correlated and investigated so normal activity can be separated from behaviour that genuinely deserves attention.
Find what matters. Ignore what does not.

03
Translate credible threats into clear action.
When suspicious activity is confirmed, NightGrid classifies and escalates it with the context your organisation needs to respond.
Act with clarity, not guesswork.
03 / THE NIGHTGRID
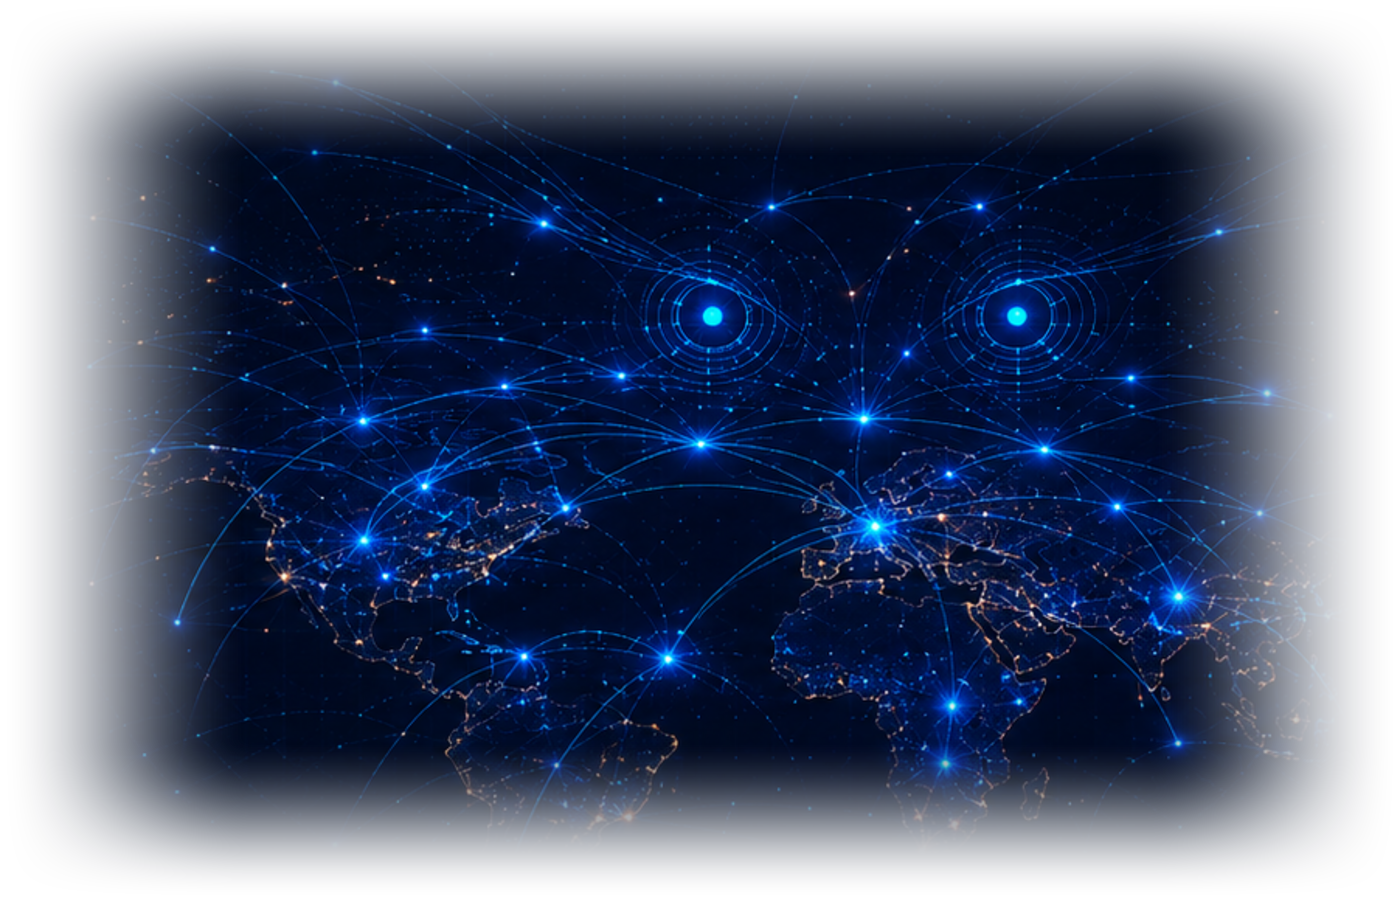
ONE ENVIRONMENT. ONE VIEW.
Endpoints. Cloud. Identity. Networks. Applications. Remote users.
NightGrid brings fragmented security activity into a continuous operational view.
“You do not need another dashboard. You need someone watching it.”
04 / HOW IT WORKS
A clear operating rhythm keeps monitoring aligned to the environment and escalation aligned to your business.

01
Work with the security technologies already protecting your organisation.

02
Bring security telemetry into one continuous operational view.

03
Correlate, prioritise and investigate activity that warrants attention.

04
Communicate credible threats through agreed response procedures.

05
Use operational insight to strengthen your defensive posture over time.
05 / HUMAN-LED OPERATIONS
Automation can process enormous volumes of security information, correlate events and surface anomalies at machine speed.
Experienced analysts provide the context needed to assess risk, prioritise response and determine what genuinely requires action.

 ANALYST COVERAGE ACTIVE
06 / WHY NIGHTGRID
Continuous oversight should make security clearer, calmer and more actionable—not add another layer of noise.
01

Seasoned analysts bring context, judgement and accountability to every investigation.
02

Continuous operations keep your environment watched across regions and time zones.
03

High-volume signals are correlated and prioritised with modern security tooling.
04

Credible threats are escalated quickly with the context your team needs to act.
05

NightGrid works with cloud, on-premise and hybrid security ecosystems.
06
Operational insight strengthens detection and response performance over time.
07 / OPERATIONAL CLARITY
KNOW WHAT IS HAPPENING, NOT JUST WHAT HAPPENED
NightGrid keeps monitored activity, investigations and security events visible so leaders and technical teams share the same operational picture.
 OPERATIONS LIVE
EVENTS ANALYSED
48.2MCONTINUOUS
INVESTIGATIONS
1,204PRIORITISED
MEAN REVIEW TIME
11mRAPID TRIAGE
COVERAGE STATUS
24/7ALWAYS ON

ILLUSTRATIVE OPERATIONS VIEW
08 / START A CONVERSATION
Plan a focused security review around your environment, existing tools, priority risks and escalation requirements.
Continuous security operations
Tell us a little about your environment, priority risks and current security operation. We will use this context to shape a focused first conversation.